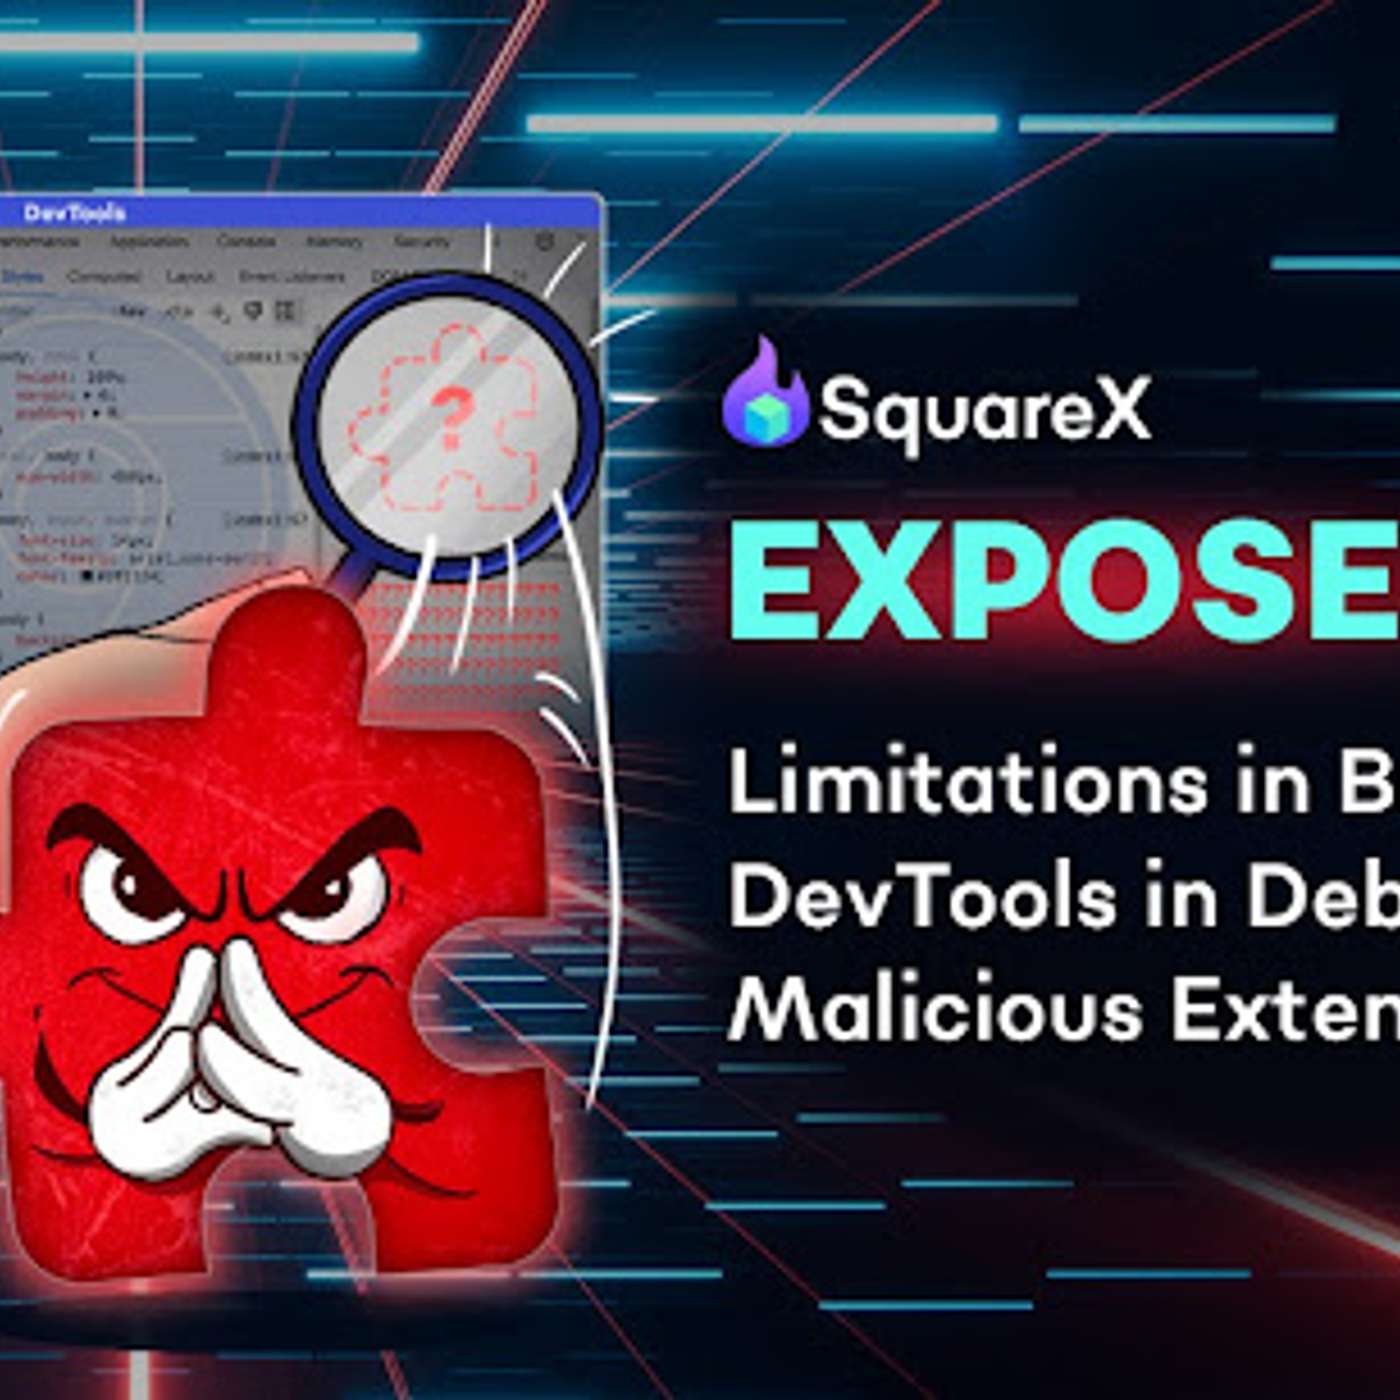
SquareX Discloses Architectural Limitations Of Browser DevTools In Debugging Malicious Extensions
This story was originally published on HackerNoon at: https://hackernoon.com/squarex-discloses-architectural-limitations-of-browser-devtools-in-debugging-malicious-extensions . In other words, even if browser vendors were not inundated by the sheer quantity of extension submission requests, the architectural limitations of Browser DevT Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity . You can also check exclusive content about #cybersecurity , #squarex , #cybernewswire , #press-release , #squarex-announcement , #cyber-security-awareness , #cyber-threats , #good-company , and more. This story was written by: @cybernewswire . Learn more about this writer by checking @cybernewswire's about page, and for more stories, please visit hackernoon.com . Despite the expanding use of browser extensions, the majority of enterprises and individuals still rely on labels such as “Verified” and “Chrome Featured” as a security indicator. The recent Geco Colorpick case exemplifies how these certifications provide nothing more than a false sense of security. Koi Research disclosed 18 malicious extensions that distributed spyware to 2.3M users.
You May Also Like
Software Testing - Qualität, Testautomatisierung & Agilität
Richard Seidl - Experte für Software-Entwicklung und Testautomatisierung

AI Fire Daily
AIFire.co

Mark Tilbury
Mark Tilbury Fan
AI News Daily
brief.news

Late Night Linux
The Late Night Linux Family

Jack Hopkins
Jack Hopkins

Artificial Intelligence Masterclass
AI Masterclass

Theo - t3․gg
Theo - t3․gg

TBPN
John Coogan & Jordi Hays

This Week in Startups
Jason Calacanis
Software Testing - Qualität, Testautomatisierung & Agilität
Richard Seidl - Experte für Software-Entwicklung und Testautomatisierung
AI Fire Daily
AIFire.co
Mark Tilbury
Mark Tilbury Fan
AI News Daily
brief.news
Late Night Linux
The Late Night Linux Family
Jack Hopkins
Jack Hopkins
Artificial Intelligence Masterclass
AI Masterclass
Theo - t3․gg
Theo - t3․gg
TBPN
John Coogan & Jordi Hays
This Week in Startups
Jason Calacanis
Community discussion