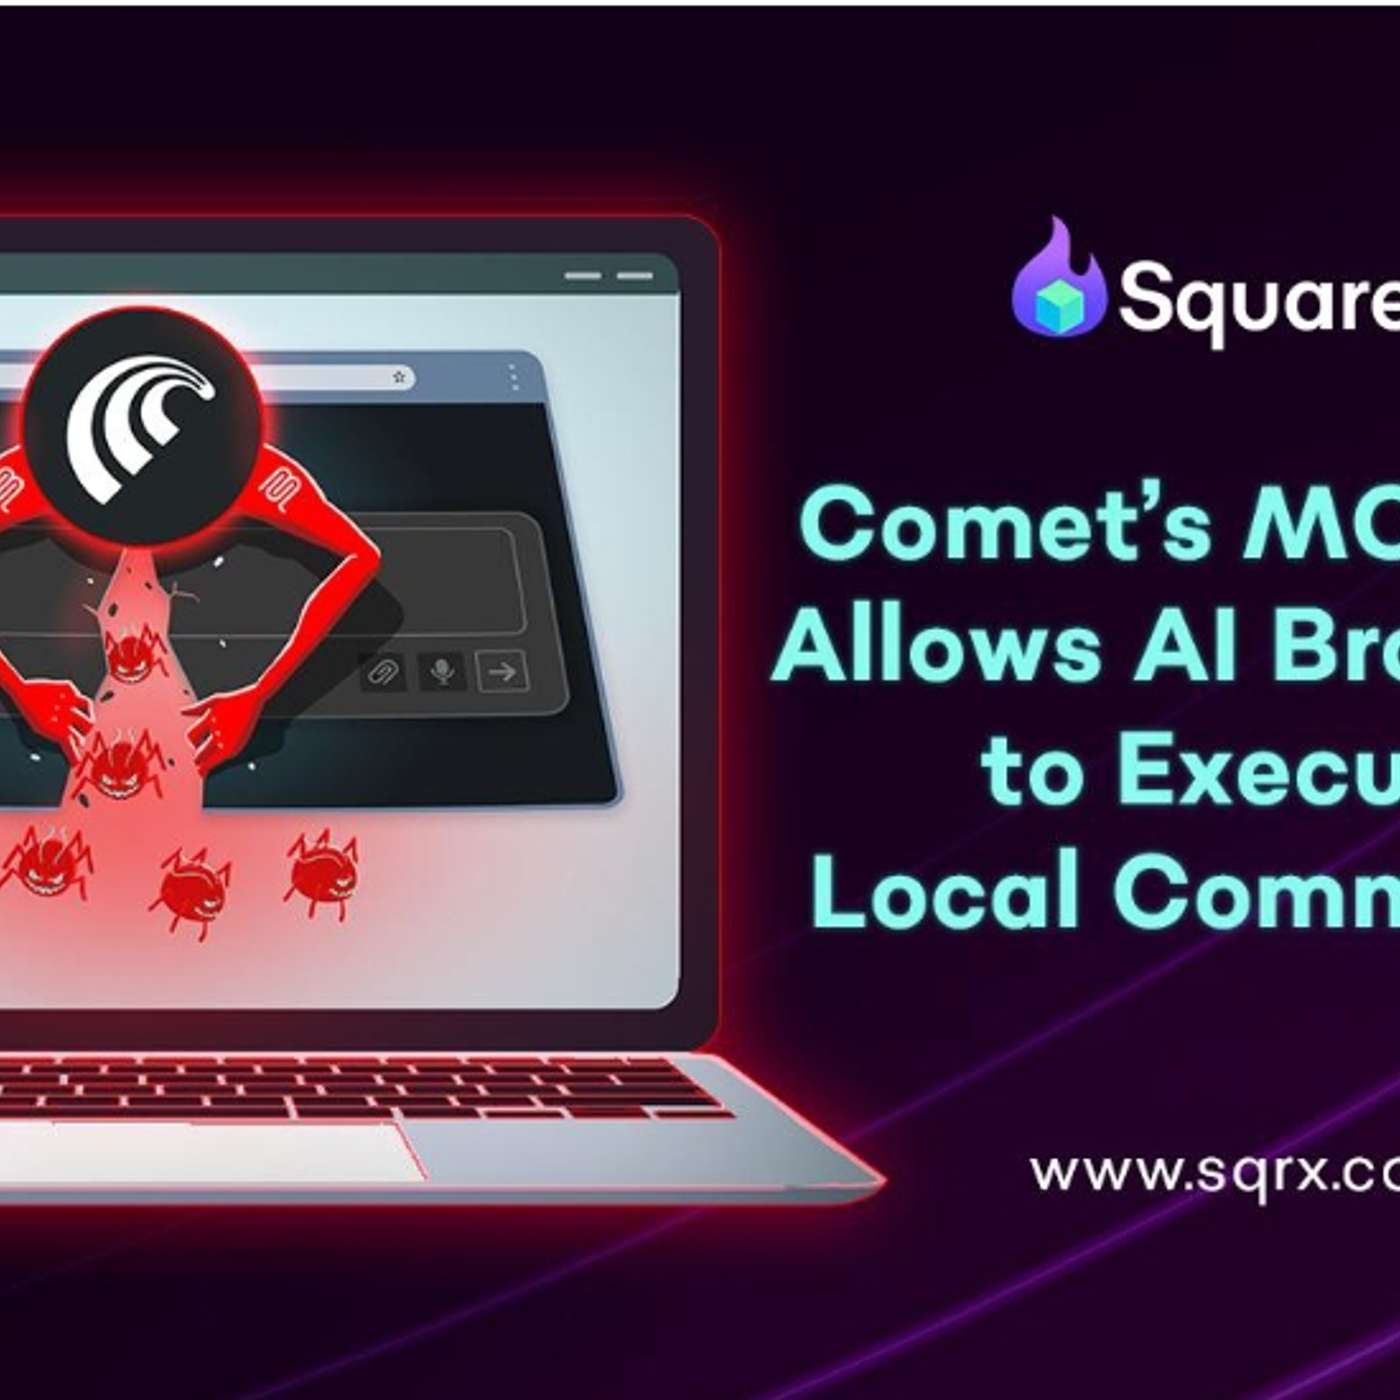
Obscure MCP API in Comet Browser Breaches User Trust, Enabling Full Device Control via AI Browsers
This story was originally published on HackerNoon at: https://hackernoon.com/obscure-mcp-api-in-comet-browser-breaches-user-trust-enabling-full-device-control-via-ai-browsers . The research reveals that Comet has implemented a MCP API (chrome.perplexity.mcp.addStdioServer) that allows its embedded extensions to execute arbitrary local Check more stories related to cybersecurity at: https://hackernoon.com/c/cybersecurity . You can also check exclusive content about #cybersecurity , #squarex , #cybernewswire , #press-release , #blockchain-development , #squarex-announcement , #crypto-exchange , #good-company , and more. This story was written by: @cybernewswire . Learn more about this writer by checking @cybernewswire's about page, and for more stories, please visit hackernoon.com . SquareX released critical research exposing a hidden API in Comet that allows extensions in the AI Browser to execute local commands and gain full control over users' devices. The research reveals that Comet has implemented a MCP API (chrome.perplexity.mcp.addStdioServer) that allows its embedded extensions to execute arbitrary local commands.
You May Also Like

Theo - t3․gg
Theo - t3․gg

All-In with Chamath, Jason, Sacks & Friedberg
All-In Podcast, LLC

Artificial Intelligence Masterclass
AI Masterclass

The Daily AI Show
The Daily AI Show Crew - Brian, Beth, Jyunmi, Andy and Karl

CriptoMonedas TV
CriptoMonedas TV

Jack Hopkins
Jack Hopkins
MacMagazine no Ar
MacMagazine.com.br
AI Unraveled: Latest AI News & Trends, ChatGPT, Gemini, DeepSeek, Gen AI, LLMs, Agents, Ethics, Bias
Etienne Noumen
AI News Daily
brief.news

Security Weekly Podcast Network (Audio)
Security Weekly Productions
Theo - t3․gg
Theo - t3․gg
All-In with Chamath, Jason, Sacks & Friedberg
All-In Podcast, LLC
Artificial Intelligence Masterclass
AI Masterclass
The Daily AI Show
The Daily AI Show Crew - Brian, Beth, Jyunmi, Andy and Karl
CriptoMonedas TV
CriptoMonedas TV
Jack Hopkins
Jack Hopkins
MacMagazine no Ar
MacMagazine.com.br
AI Unraveled: Latest AI News & Trends, ChatGPT, Gemini, DeepSeek, Gen AI, LLMs, Agents, Ethics, Bias
Etienne Noumen
AI News Daily
brief.news
Security Weekly Podcast Network (Audio)
Security Weekly Productions
Community discussion