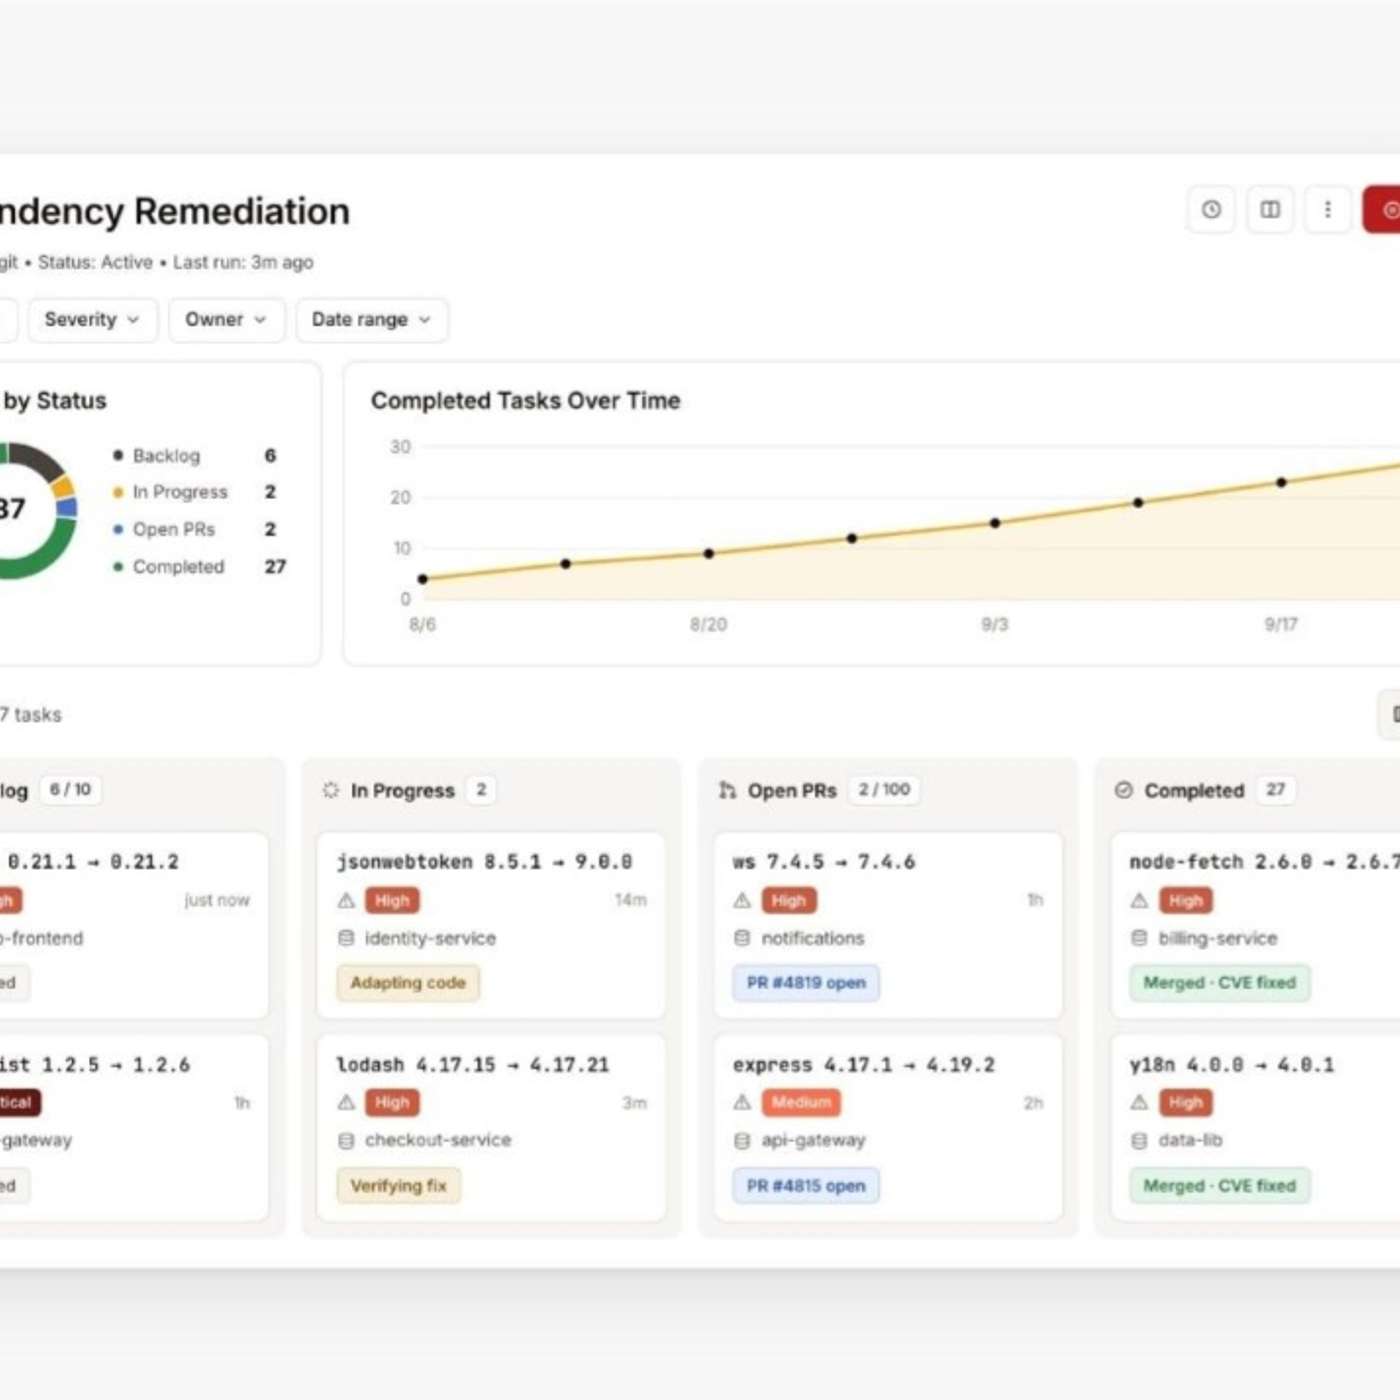
Legit Security Launches Agentic Remediation for Open-Source Dependency Vulnerabilities
This story was originally published on HackerNoon at: https://hackernoon.com/legit-security-launches-agentic-remediation-for-open-source-dependency-vulnerabilities.
The expansion addresses a growing gap in application security: as AI-generated code accelerates software delivery, most modern codebases are made up largely of
Check more stories related to undefined at: https://hackernoon.com/c/undefined. You can also check exclusive content about #cybersecurity, #cyber-threats, #cybernewswire, #press-release, #cybercrime, #cyber-attack, #cybersecurity-tips, #good-company, and more.
This story was written by: @cybernewswire. Learn more about this writer by checking @cybernewswire's about page, and for more stories, please visit hackernoon.com.
Legit Security expanded its Agentic Remediation capability to cover vulnerabilities in open-source dependencies, enabling development teams to move from detection to a verified fix without manual triage. The expansion addresses a growing gap in application security, where traditional workflows can't keep pace with the volume of vulnerabilities introduced through dependencies.
You May Also Like
The Times Tech Podcast
The Sunday Times

Theo - t3․gg
Theo - t3․gg
The Deep Dive Radio Show and Nick's Nerd News
Nick Espinosa, Chief Security Fanatic
Elon Musk Podcast
Stage Zero

Jack Hopkins
Jack Hopkins
Engadget News + Next
Engadget
TBPN
John Coogan & Jordi Hays
The Everything Feed - All Packet Pushers Pods
Packet Pushers Team

Mark Tilbury
Mark Tilbury Fan

The Daily AI Show
The Daily AI Show Crew - Brian, Beth, Jyunmi, Andy and Karl
The Times Tech Podcast
The Sunday Times
Theo - t3․gg
Theo - t3․gg
The Deep Dive Radio Show and Nick's Nerd News
Nick Espinosa, Chief Security Fanatic
Elon Musk Podcast
Stage Zero
Jack Hopkins
Jack Hopkins
Engadget News + Next
Engadget
TBPN
John Coogan & Jordi Hays
The Everything Feed - All Packet Pushers Pods
Packet Pushers Team
Mark Tilbury
Mark Tilbury Fan
The Daily AI Show
The Daily AI Show Crew - Brian, Beth, Jyunmi, Andy and Karl
Community discussion