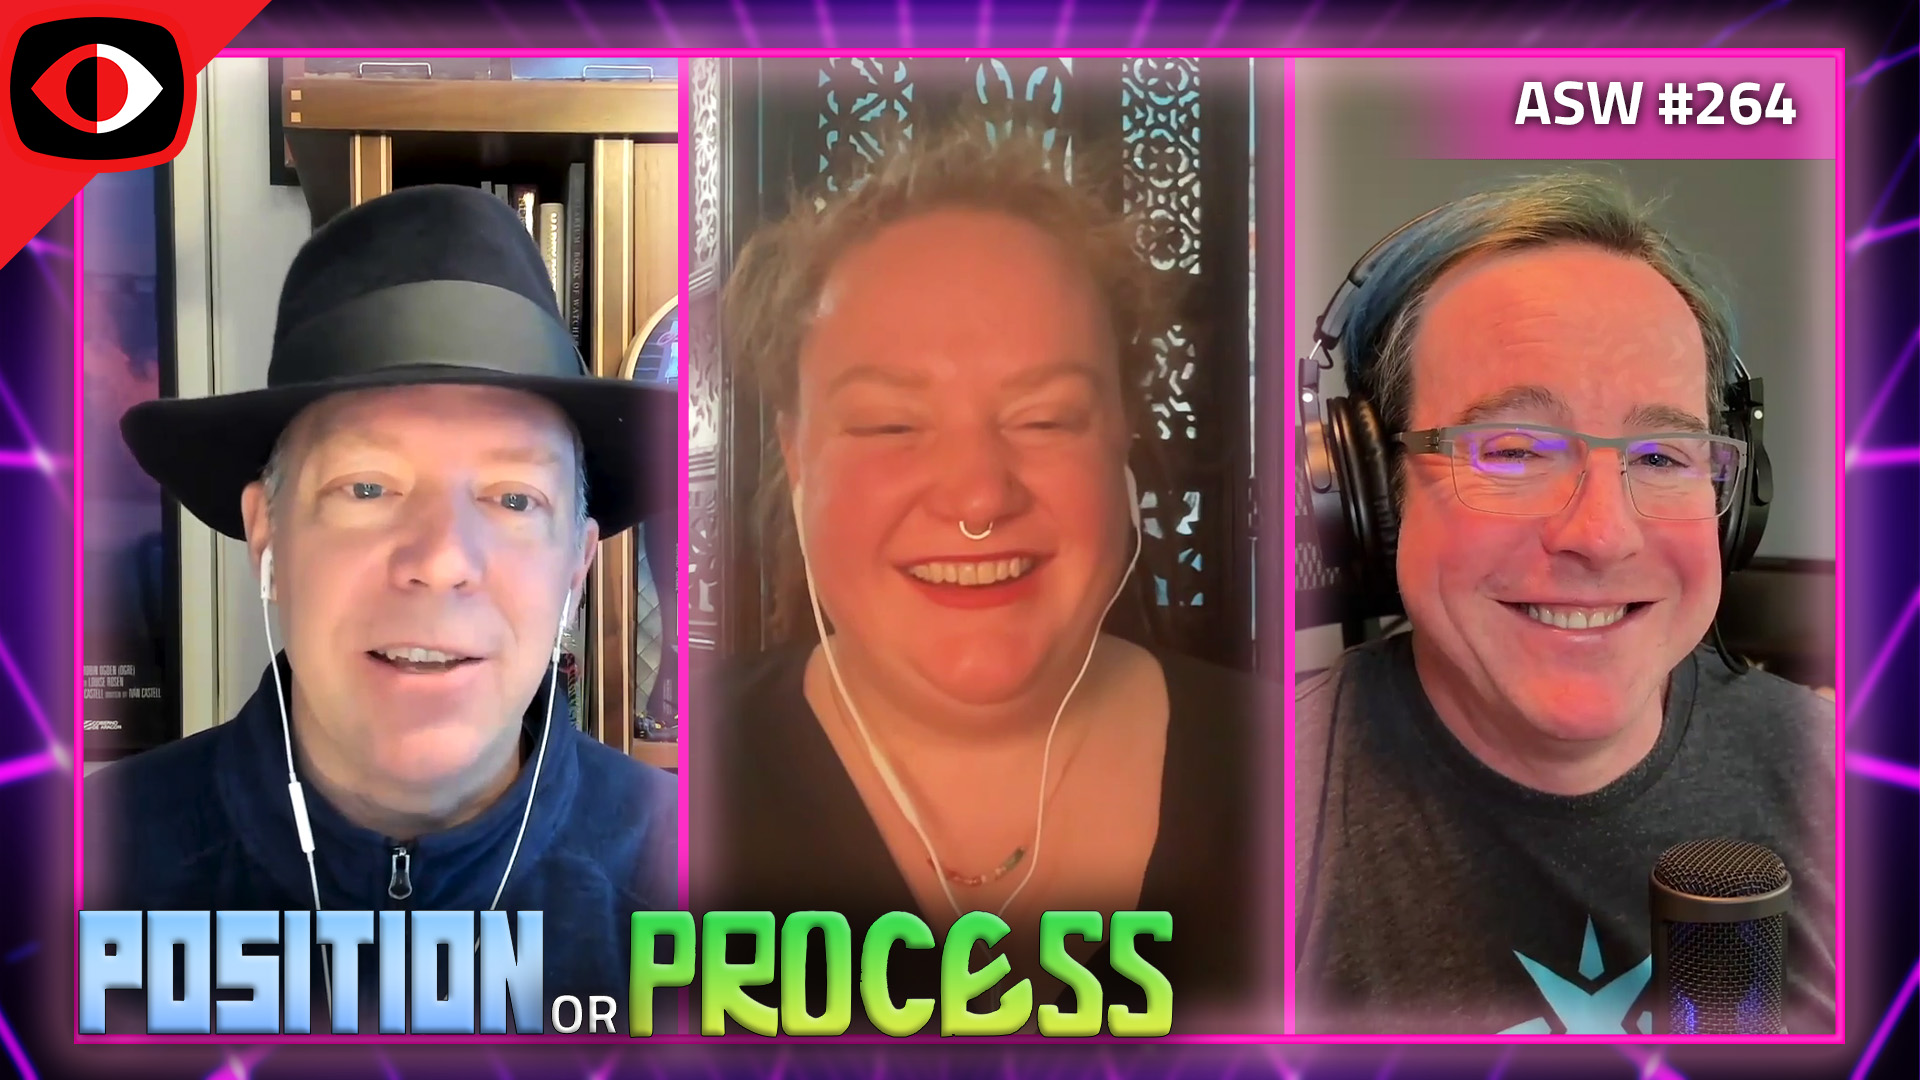
Starting with Appsec -- Is It More of a Position or a Process? - ASW #264
This year we've talked about vulns, clouds, breaches, presentations, and all the variations of Dev, Sec, and Ops. As we end the year, let's talk about starting things -- like starting an appsec program or an appsec career. But is there still a need for an appsec team? Or has it turned into specializations for areas like cloud security and bug bounty programs? We'll cover careers and coding, with an eye towards figuring out what modern software development looks like and where application (or product!) security fits in that model.
Segment resources
- https://owaspsamm.org
- https://www.microsoft.com/en-us/security/blog/2023/11/02/announcing-microsoft-secure-future-initiative-to-advance-security-engineering/
- https://www.cisa.gov/resources-tools/resources/secure-by-design
Weak randomness in old JavaScript crypto, lack of encryption in purported end-to-end encryption, a platform engineering maturity model, PyPI's first security audit, vision for a Rust specification, and more!
Visit https://securityweekly.com/asw for all the latest episodes!
Follow us on Twitter: https://www.twitter.com/secweekly
Like us on Facebook: https://www.facebook.com/secweekly
Visit https://securityweekly.com/asw for all the latest episodes!
Follow us on Twitter: https://www.twitter.com/secweekly
Like us on Facebook: https://www.facebook.com/secweekly
Show Notes: https://securityweekly.com/asw-264
You May Also Like
Stephan Livera Podcast
Stephan Livera
Syntax - Tasty Web Development Treats
Wes Bos & Scott Tolinski - Full Stack JavaScript Web Developers

Jack Hopkins
Jack Hopkins

AI Fire Daily
AIFire.co

a16z Show
Andreessen Horowitz

Taylor Lorenz’s Power User
Taylor Lorenz

Tech Update | BNR
BNR Nieuwsradio
Chat GPT Infinite Intelligence
Sol Good Network

ChatGPT - Sol Good Shorts
Sol Good Network

Mark Tilbury
Mark Tilbury Fan
Stephan Livera Podcast
Stephan Livera
Syntax - Tasty Web Development Treats
Wes Bos & Scott Tolinski - Full Stack JavaScript Web Developers
Jack Hopkins
Jack Hopkins
AI Fire Daily
AIFire.co
a16z Show
Andreessen Horowitz
Taylor Lorenz’s Power User
Taylor Lorenz
Tech Update | BNR
BNR Nieuwsradio
Chat GPT Infinite Intelligence
Sol Good Network
ChatGPT - Sol Good Shorts
Sol Good Network
Mark Tilbury
Mark Tilbury Fan
Community discussion