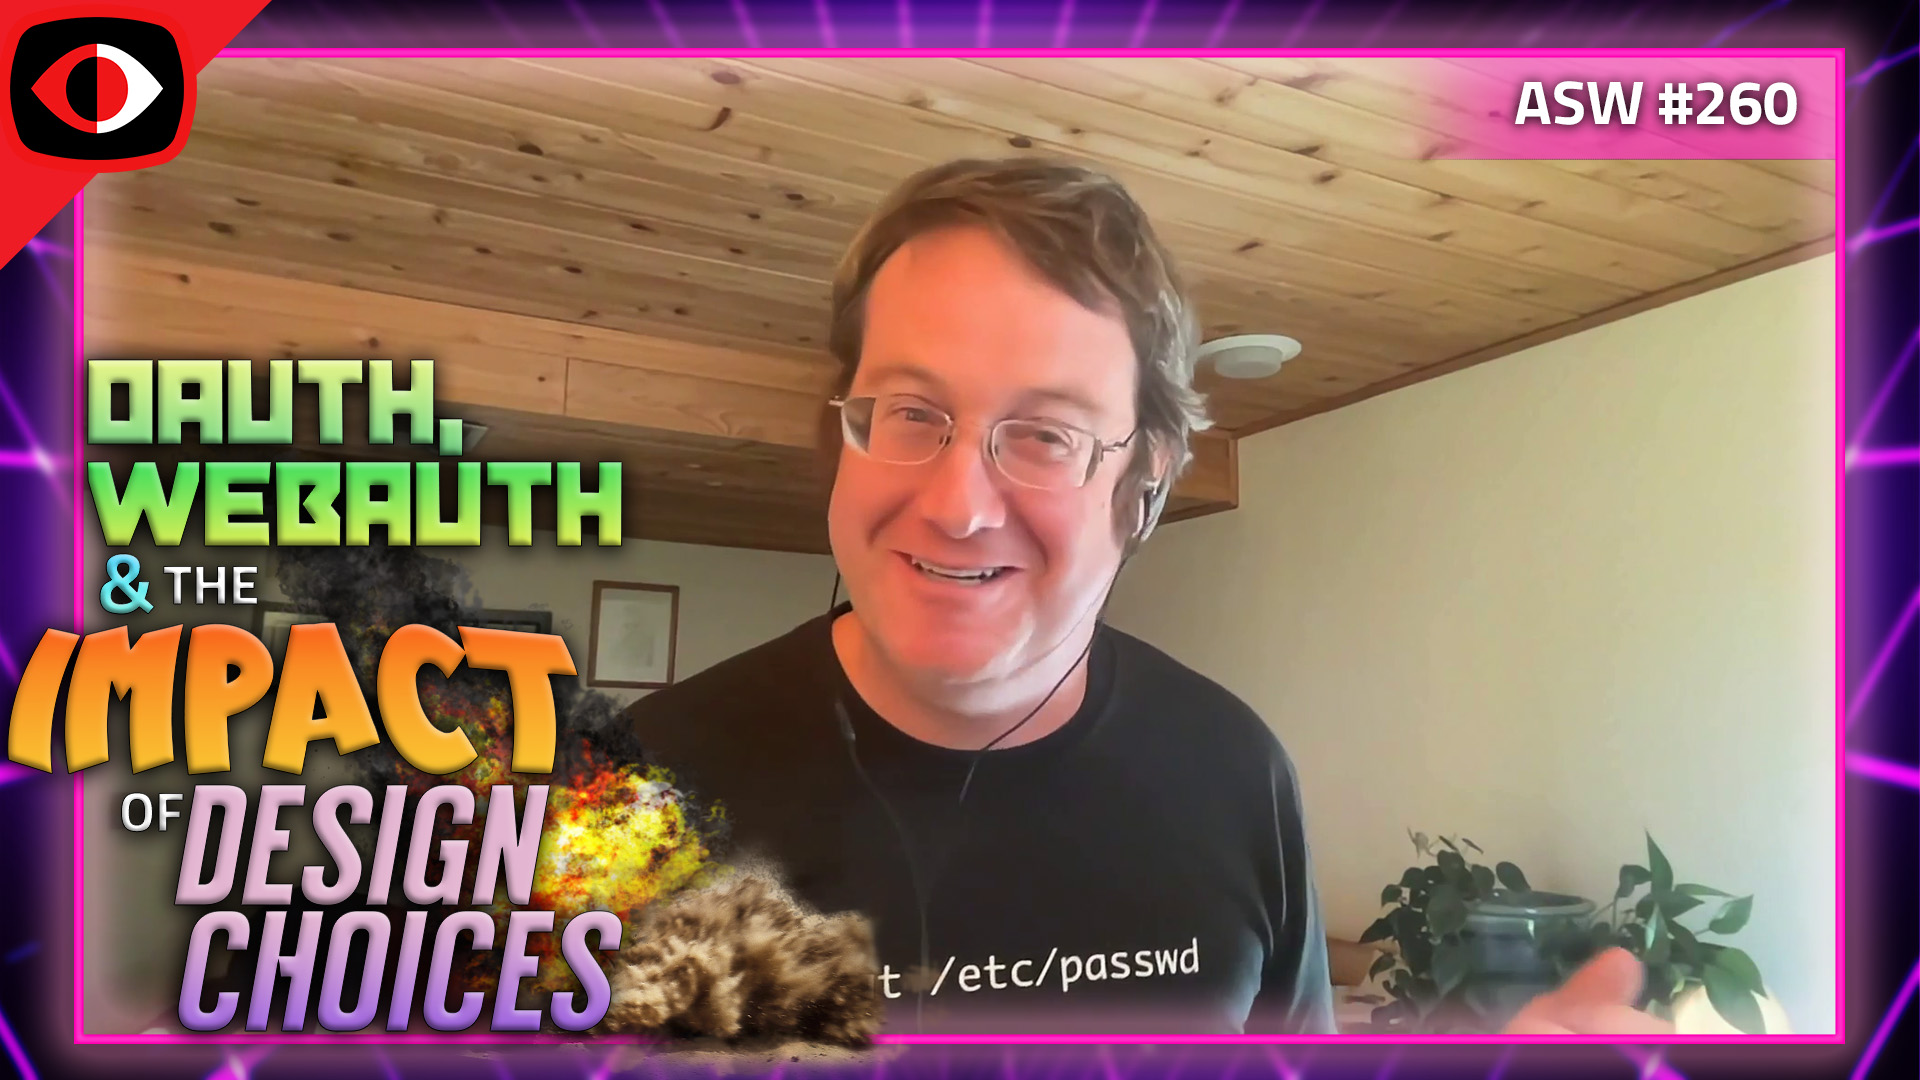
OAuth, WebAuthn, & The Impact of Design Choices - Dan Moore - ASW #260
We return to discussions of OAuth and all sorts of authentication. This time around we're looking at the design of authentication protocols, the kinds of trade-offs they weigh for adoption and security, and how a standard evolves over time to keep pace with new attacks and put to rest old mistakes.
Segment resources:
- https://fusionauth.io/docs/v1/tech/core-concepts/modes
- https://webauthn.wtf/
- https://datatracker.ietf.org/doc/html/rfc7636
- https://www.ietf.org/about/participate/tao/
In the news, appsec lessons from the Okta breach, directory traversal (and appsec) lessons from SolarWinds, how CISOs and Boards rank factors around vulns and patching, revisiting cryptocurrency attacks for lessons in business logic and threat modeling, CISA and friends update guidance on Secure Design, and more!
Visit https://securityweekly.com/asw for all the latest episodes!
Follow us on Twitter: https://www.twitter.com/secweekly
Like us on Facebook: https://www.facebook.com/secweekly
Show Notes: https://securityweekly.com/asw-260
You May Also Like
Programming Tech Brief By HackerNoon
HackerNoon

Artificial Intelligence Masterclass
AI Masterclass

The Good Tech Companies
HackerNoon

Engadget News + Next
Engadget
Thinking Crypto News & Interviews
Tony Edward

Two Blokes Talking Tech
Trevor Long and Stephen Fenech
Stephan Livera Podcast
Stephan Livera
Syntax - Tasty Web Development Treats
Wes Bos & Scott Tolinski - Full Stack JavaScript Web Developers

Jack Hopkins
Jack Hopkins

AI Fire Daily
AIFire.co
Programming Tech Brief By HackerNoon
HackerNoon
Artificial Intelligence Masterclass
AI Masterclass
The Good Tech Companies
HackerNoon
Engadget News + Next
Engadget
Thinking Crypto News & Interviews
Tony Edward
Two Blokes Talking Tech
Trevor Long and Stephen Fenech
Stephan Livera Podcast
Stephan Livera
Syntax - Tasty Web Development Treats
Wes Bos & Scott Tolinski - Full Stack JavaScript Web Developers
Jack Hopkins
Jack Hopkins
AI Fire Daily
AIFire.co
Community discussion