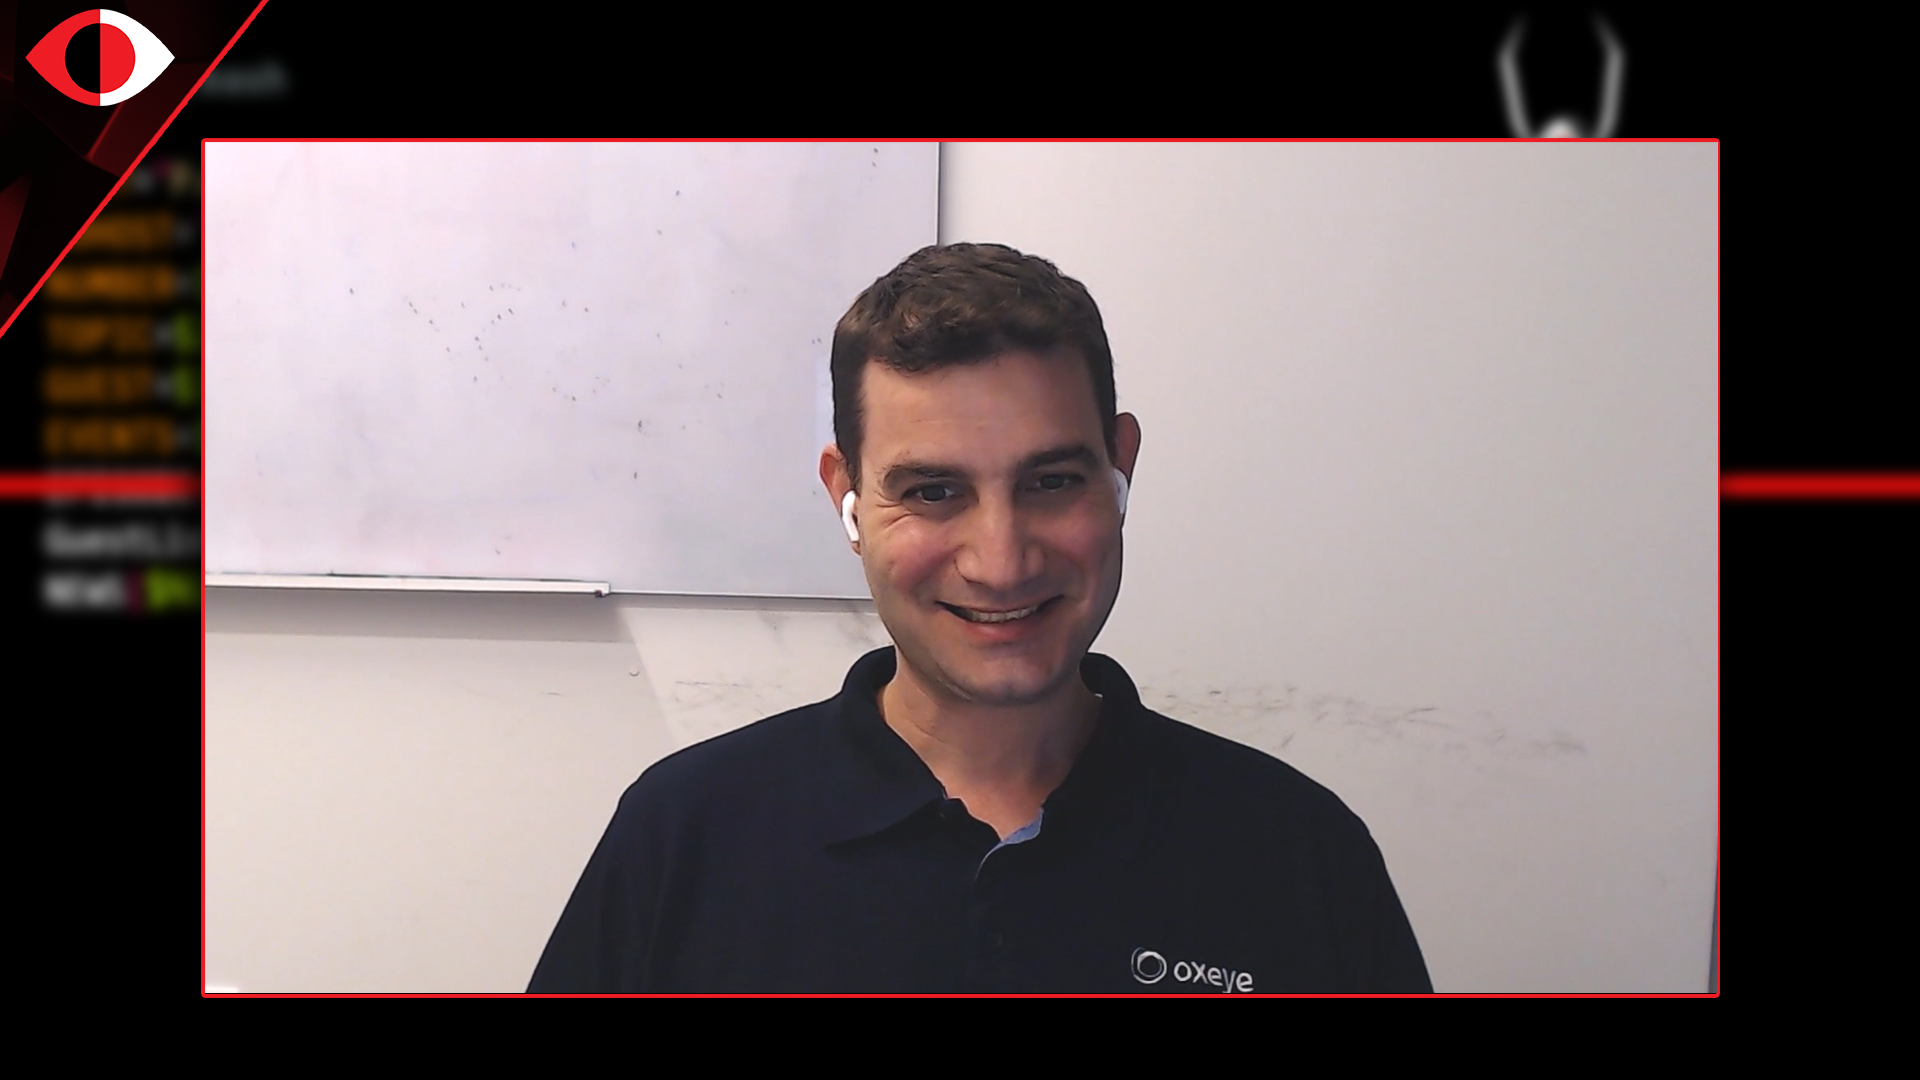
ASW #214 - Dean Agron
The core focus of this podcast is to provide the listeners with food for thoughts for what is required for releasing secured cloud native applications - Continuous, Multi-layer, and Multi-service analysis and focusing not only on the code, but also on the runtime and the infrastructure. - Focus on the vulnerabilities that matter. The critical, exploitable ones. Use Context. - Choose the right remediation forms. It may come in different shapes Segment Resources: Oxeye Website for videos and content - www.oxeye.io Exchange RCE, bulk pull requests to patch at scale, metrics from DORA, best papers from USENIX, implementing passkeys Visit https://www.securityweekly.com/asw for all the latest episodes! Follow us on Twitter: https://www.twitter.com/secweekly Like us on Facebook: https://www.facebook.com/secweekly Show Notes: https://securityweekly.com/asw214
You May Also Like

Mark Tilbury
Mark Tilbury Fan
Applelianos
Applelianos

Jack Hopkins
Jack Hopkins

Theo - t3․gg
Theo - t3․gg

Jak Piggott
Jak Piggott

Engadget News + Next
Engadget

TBPN
John Coogan & Jordi Hays
Material
Relay

The Vergecast
The Verge

The Deep Dive Radio Show and Nick's Nerd News
Nick Espinosa, Chief Security Fanatic
Mark Tilbury
Mark Tilbury Fan
Applelianos
Applelianos
Jack Hopkins
Jack Hopkins
Theo - t3․gg
Theo - t3․gg
Jak Piggott
Jak Piggott
Engadget News + Next
Engadget
TBPN
John Coogan & Jordi Hays
Material
Relay
The Vergecast
The Verge
The Deep Dive Radio Show and Nick's Nerd News
Nick Espinosa, Chief Security Fanatic
Community discussion