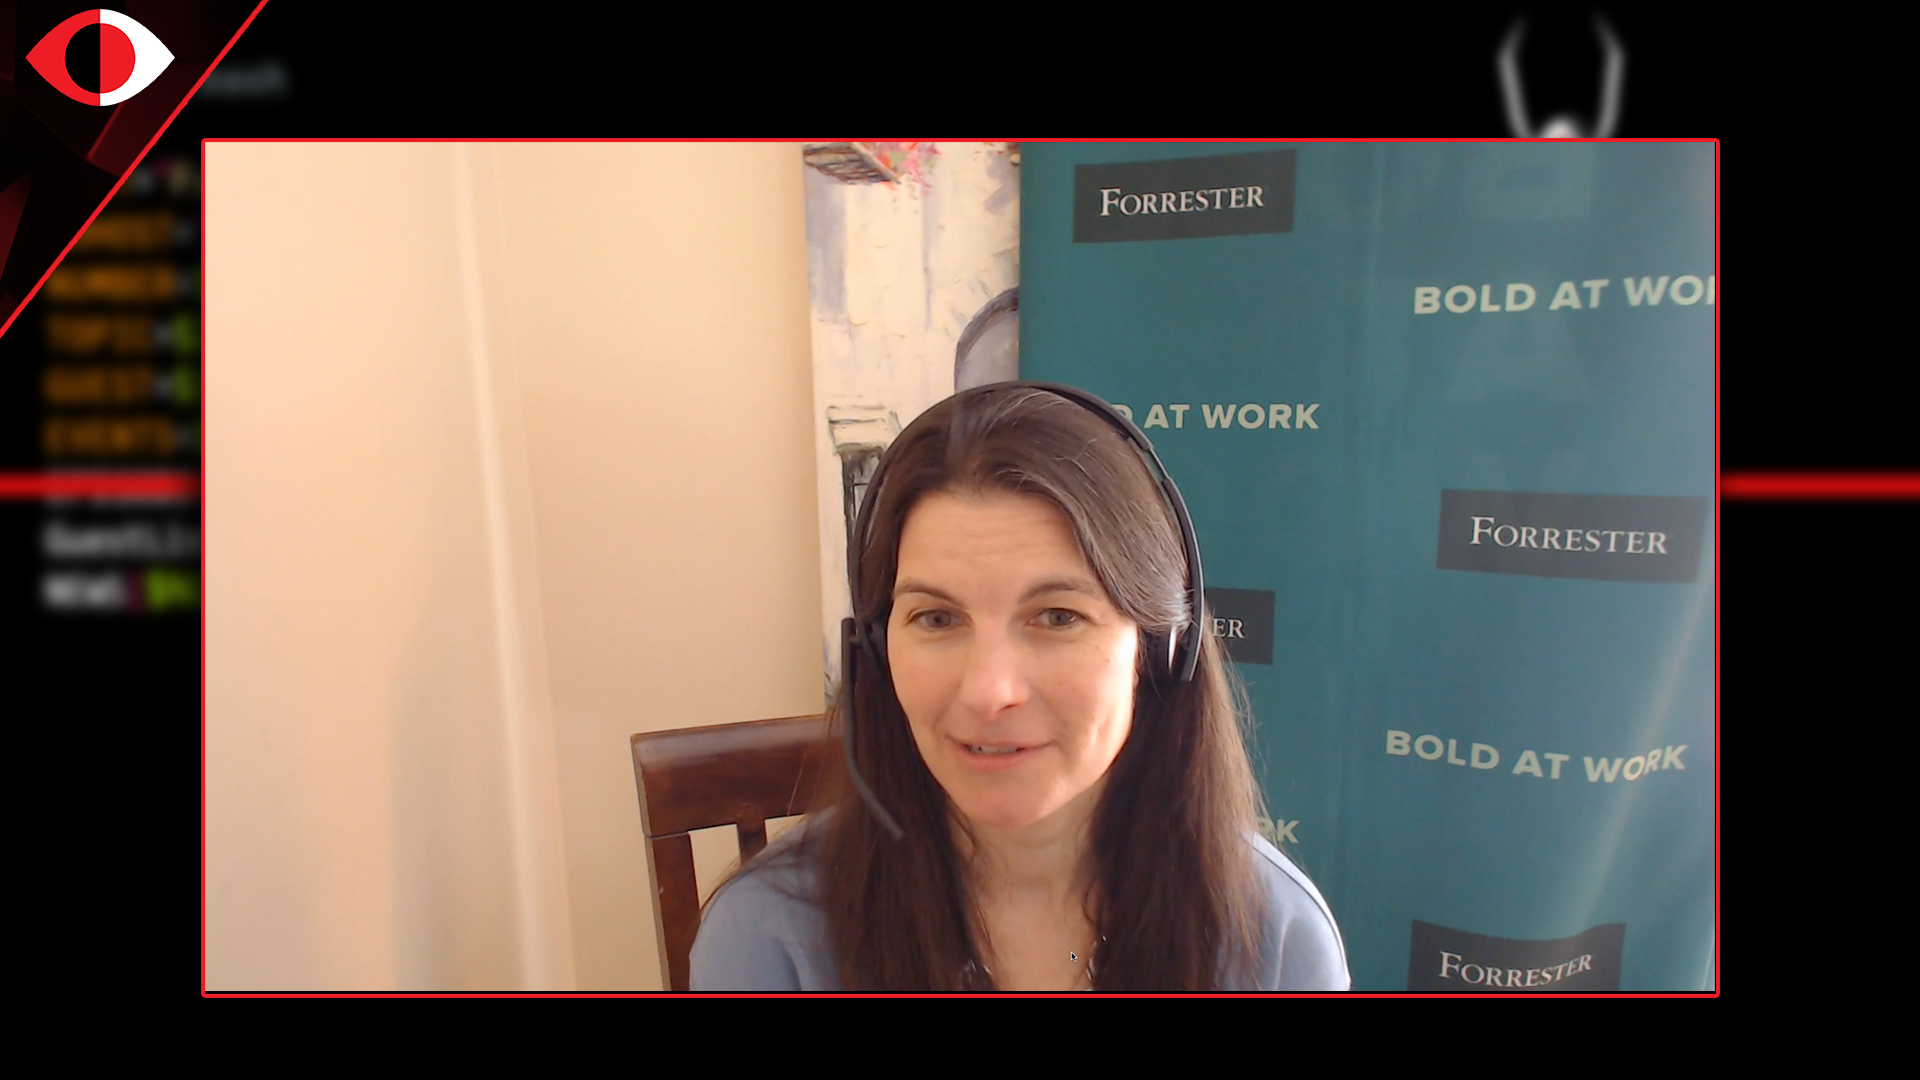
ASW #213 - Janet Worthington
Applications are the most frequent external attack vector for companies. However, application security can improve only if developers either code securely or remediate existing security flaws — unfortunately, many don’t receive training with proper security know-how. In this session, we will talk about the state of application security education and what you can do to secure what you sell. Segment Resources: - https://www.forrester.com/blogs/school-is-in-session-but-appsec-is-still-on-vacation/?ref_search=3502061_1663615159889 https://www.wisporg.com/events-calendar/2022/11/8/security-amp-risk-conference-forrester https://www.veracode.com/events/hacker-games https://blogs.microsoft.com/blog/2021/10/28/america-faces-a-cybersecurity-skills-crisis-microsoft-launches-national-campaign-to-help-community-colleges-expand-the-cybersecurity-workforce/ Wiz reveals authorization bypass in Oracle Cloud, Python 15-year old path traversal flaw, Prototype Pollution in Chrome, PS4 flaw reappears in PS5, Why security products fail Visit https://www.securityweekly.com/asw for all the latest episodes! Follow us on Twitter: https://www.twitter.com/secweekly Like us on Facebook: https://www.facebook.com/secweekly Show Notes: https://securityweekly.com/asw213
You May Also Like
Monde Numérique (Actu Tech)
Jerome Colombain

Artificial Intelligence Masterclass
AI Masterclass
The Times Tech Podcast
The Sunday Times

Mark Tilbury
Mark Tilbury Fan
Applelianos
Applelianos
Hack és Lángos
Hack és Lángos

Jack Hopkins
Jack Hopkins

Security Weekly Podcast Network (Video)
Security Weekly Productions

Theo - t3․gg
Theo - t3․gg

Jak Piggott
Jak Piggott
Monde Numérique (Actu Tech)
Jerome Colombain
Artificial Intelligence Masterclass
AI Masterclass
The Times Tech Podcast
The Sunday Times
Mark Tilbury
Mark Tilbury Fan
Applelianos
Applelianos
Hack és Lángos
Hack és Lángos
Jack Hopkins
Jack Hopkins
Security Weekly Podcast Network (Video)
Security Weekly Productions
Theo - t3․gg
Theo - t3․gg
Jak Piggott
Jak Piggott
Community discussion