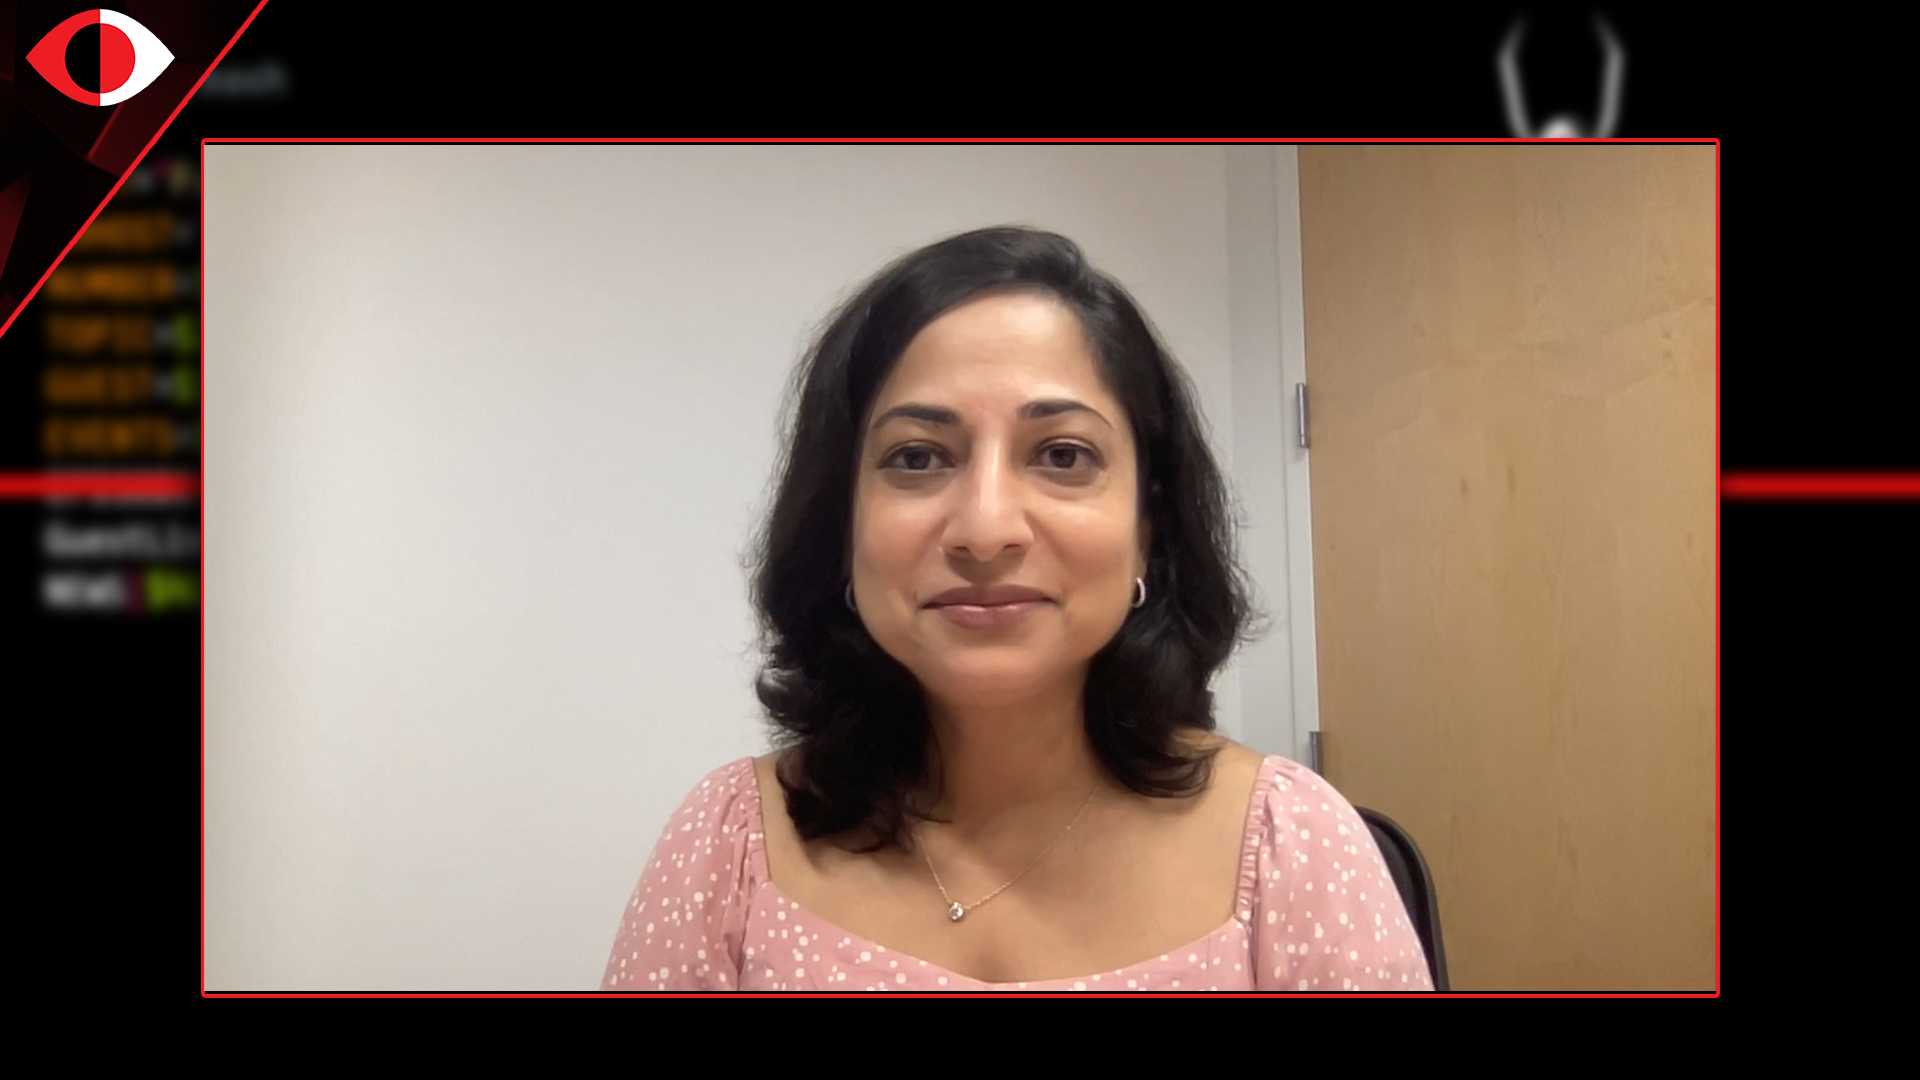
ASW #211 - Sonali Shah
Go releases their own curated vuln management resources, OSS-Fuzz finds command injection, Microsoft gets rid of Basic Auth in Exchange, NSA provides guidance on securing SDLC practices, reflections on pentesting, comments on e2e Shifting left has been a buzzword in the application security space for several years now, and with good reason – making security an integral part of development is the only practical approach for modern agile workflows. But in their drive to build security testing into development as early as possible, many organizations are neglecting application security in later phases and losing sight of the big picture. In this talk, Invicti’s Chief Product Officer Sonali Shah discusses the challenges and misunderstandings around shifting left, and provides tips on how organizations can implement web application security program without tradeoffs throughout the whole application security lifecycle. This segment is sponsored by Invicti. Visit https://securityweekly.com/invicti to learn more about them! Visit https://www.securityweekly.com/asw for all the latest episodes! Follow us on Twitter: https://www.twitter.com/secweekly Like us on Facebook: https://www.facebook.com/secweekly Show Notes: https://securityweekly.com/asw211
You May Also Like

Jack Hopkins
Jack Hopkins
The Stack Overflow Podcast
The Stack Overflow Podcast
Monde Numérique (Actu Tech)
Jerome Colombain

TBPN
John Coogan & Jordi Hays

Artificial Intelligence Masterclass
AI Masterclass
The Times Tech Podcast
The Sunday Times

Mark Tilbury
Mark Tilbury Fan
Applelianos
Applelianos
Hack és Lángos
Hack és Lángos

Security Weekly Podcast Network (Video)
Security Weekly Productions
Jack Hopkins
Jack Hopkins
The Stack Overflow Podcast
The Stack Overflow Podcast
Monde Numérique (Actu Tech)
Jerome Colombain
TBPN
John Coogan & Jordi Hays
Artificial Intelligence Masterclass
AI Masterclass
The Times Tech Podcast
The Sunday Times
Mark Tilbury
Mark Tilbury Fan
Applelianos
Applelianos
Hack és Lángos
Hack és Lángos
Security Weekly Podcast Network (Video)
Security Weekly Productions
Community discussion