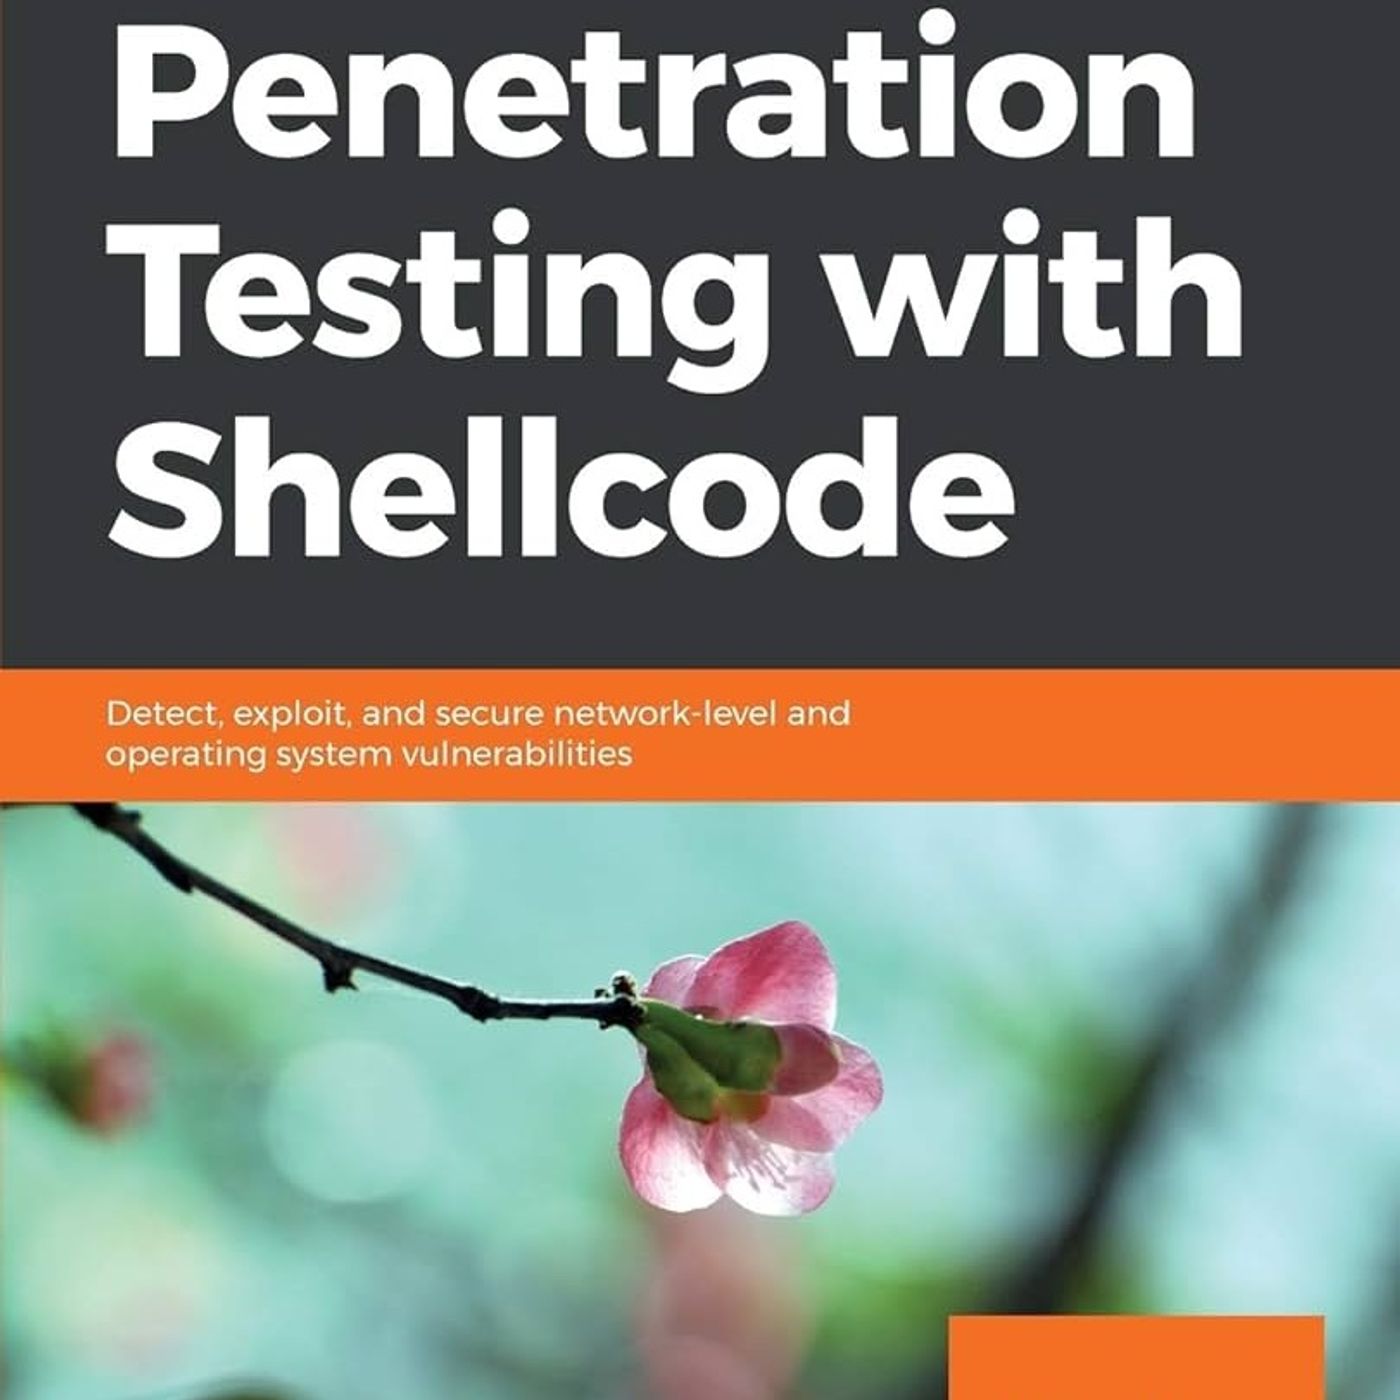
Penetration Testing with Shellcode
The Book titled "Penetration Testing with Shellcode" by Hamza Megahed. This book provides a comprehensive guide to detecting, exploiting, and securing network-level and operating system vulnerabilities. The book explores the concept of shellcode, a payload used to execute commands on a compromised system, and how it is utilized in buffer overflow attacks. It guides readers through the process of creating custom shellcode, overcoming challenges posed by bad characters, and understanding the techniques behind various shellcode types, including the execve syscall, bind TCP shell, and reverse TCP shell. The book further delves into buffer overflow attacks on both Linux and Windows systems, covering techniques like fuzzing, controlling the instruction pointer, and injecting shellcode. It also examines advanced techniques like return-oriented programming (ROP) and structured exception handling (SEH) for bypassing system security measures. The book concludes with a discussion of security mechanisms, such as ASLR and executable-space protection, that aim to prevent such attacks. You can listen and download our episodes for free on more than 10 different platforms: https://linktr.ee/cyber_security_summary Get the Book now from Amazon: https://www.amazon.com/Penetration-Testing-Shellcode-network-level-vulnerabilities/dp/1788473736?&linkCode=ll1&tag=cvthunderx-20&linkId=36d0902b6912d32c9f45c44a60d3eb51&language=en_US&ref_=as_li_ss_tl Discover our free courses in tech and cybersecurity, Start learning today: https://linktr.ee/cybercode_academy
You May Also Like

Busy Girls Book Club
Busy Girls Book Club
The Von Haessler Doctrine
Cox Media Group

Writing About Dragons and Shit
Writing About Dragons and Shit
dc
Salai Dawtcemsang
Podcast Patapoe
0d0a
The FrogPants Studios Ultra Feed!
Scott Johnson

The CVH Podcast
Christian Van Horn
Choice Classic Radio Detectives | Old Time Radio
Choice Classic Radio
Tony Katz Today
Tony Katz
All Of It
WNYC
Busy Girls Book Club
Busy Girls Book Club
The Von Haessler Doctrine
Cox Media Group
Writing About Dragons and Shit
Writing About Dragons and Shit
dc
Salai Dawtcemsang
Podcast Patapoe
0d0a
The FrogPants Studios Ultra Feed!
Scott Johnson
The CVH Podcast
Christian Van Horn
Choice Classic Radio Detectives | Old Time Radio
Choice Classic Radio
Tony Katz Today
Tony Katz
All Of It
WNYC
Community discussion